Table of Contents
Hush Entitlements adds access context to every NHI and AI agent
Finding an AI agent is only the beginning.
Agents don’t work alone. They reach your cloud services, data, and infrastructure through credentials and non-human identities (NHIs), and the access granted to those identities determines how far an agent can go. An agent with read access to a development bucket is a very different risk from an agent running as an identity with administrative access to production.
Discovery tells you the agent exists. Entitlements reveal the access behind it.
An Agent Is Only as Powerful as Its Identity
Agents are built to act. They choose tools, call systems, and take steps toward a goal. That means the real security boundary isn’t only what you expect an agent to do. It’s what the identities within its reach allow it to do.
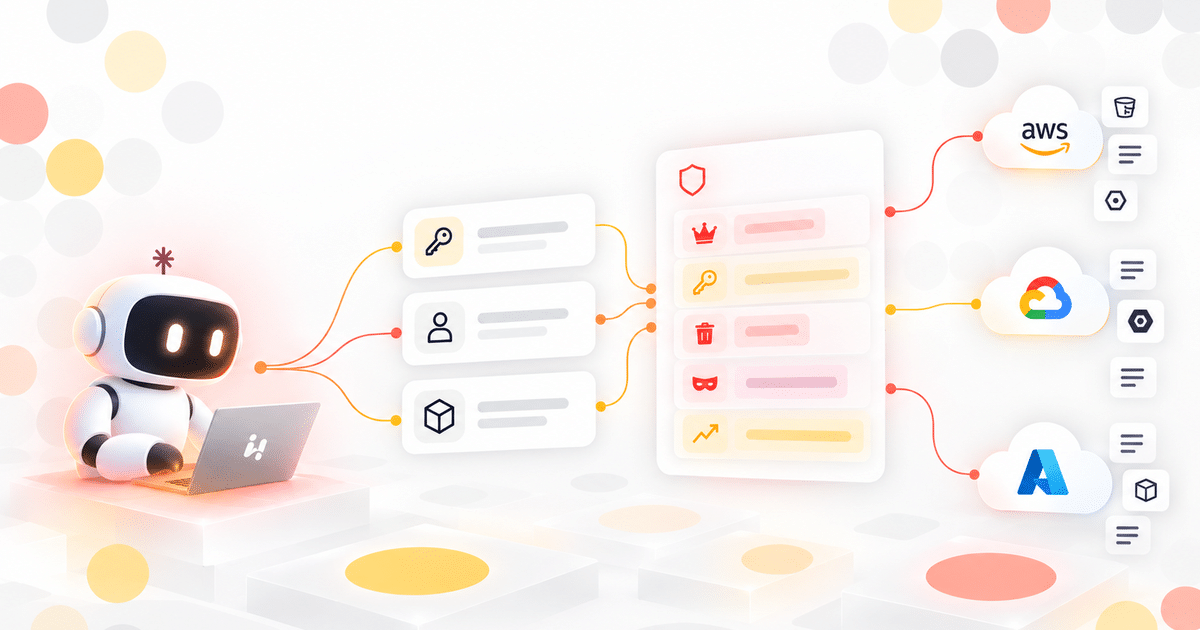
Hush discovers AI agents and MCP servers through runtime activity, including those missing from official inventories, and connects them to the credentials and identities they rely on. With Entitlements, you can now see the access behind each of those identities.
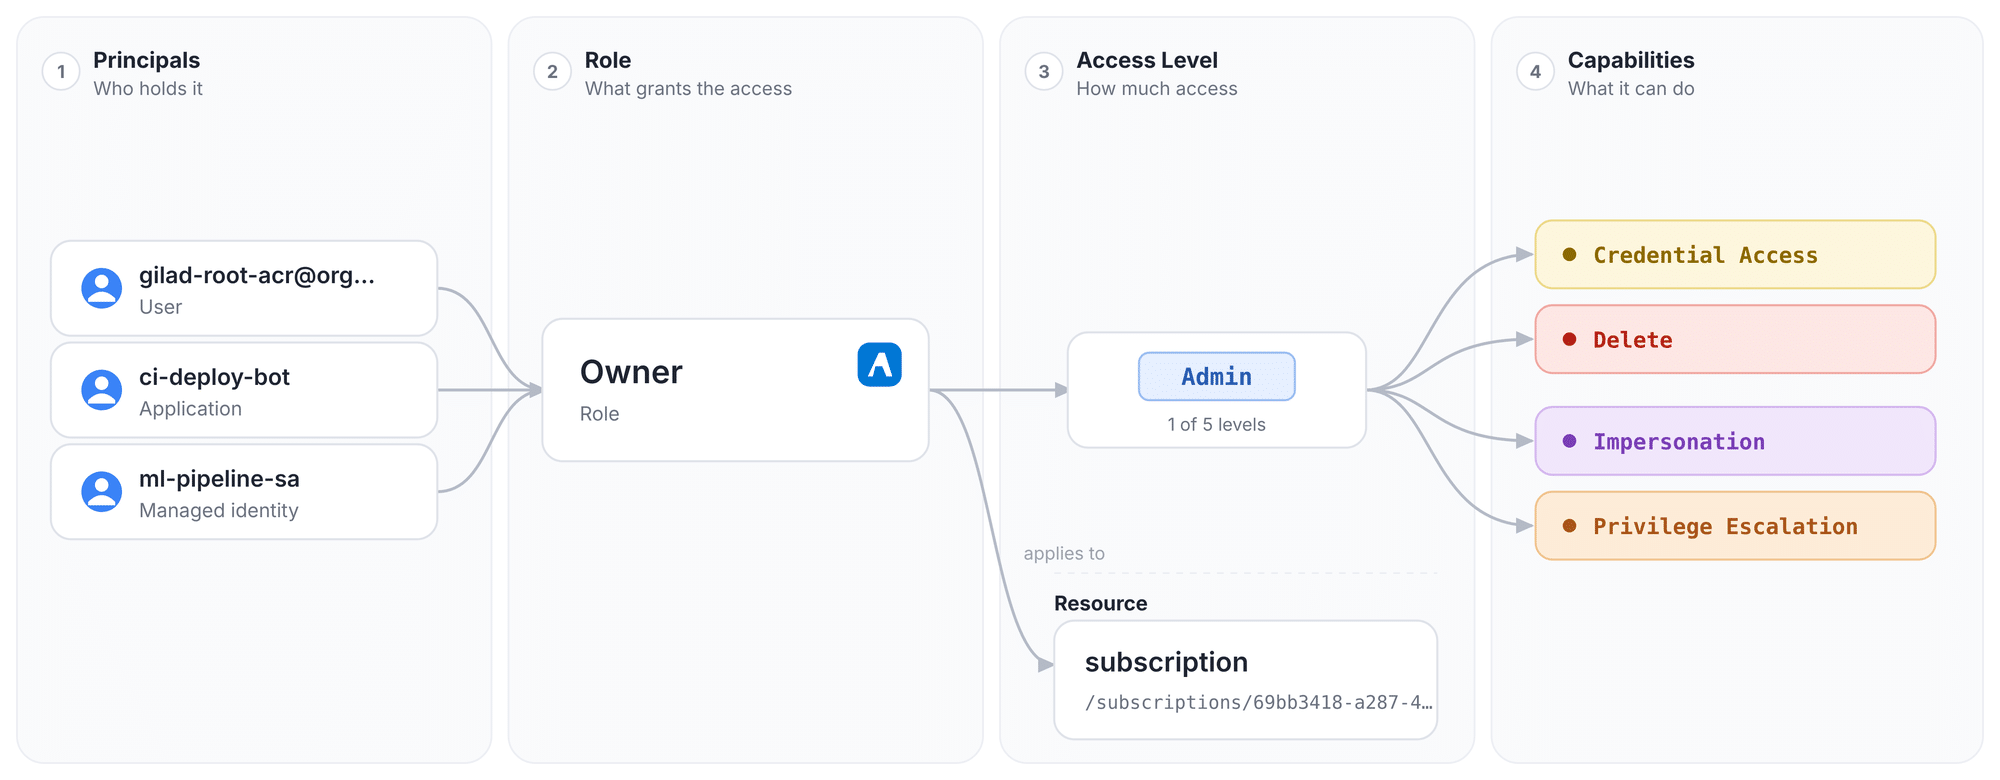
Knowing that an agent uses a service account tells you very little on its own. What matters is the access that service account carries: whether it can read a single resource, or administer production, delete data, and impersonate other identities. Entitlements provide that context, helping you understand how far an agent’s reach could extend.
From a List of Identities to a Picture of Power
Cloud environments run on a growing number of machine identities: service accounts, workload identities, IAM roles, managed identities, and more. Hush already discovers them and ties them to the credentials and workloads that use them. Entitlements add the missing piece: what each identity is actually allowed to do.
Hush Entitlements provides visibility into cloud roles, policies, and permissions across AWS, GCP, and Azure. It connects that access to the identities that hold it, showing what each identity can do, which sensitive capabilities it has, and where its permissions apply – from individual resources to entire cloud accounts and organizations.
This gives security teams a clear view of privileged access across their environment, without having to piece together IAM configurations from multiple cloud consoles.
A service account stops being another line in an inventory. You know whether it can read one resource or administer your production environment, and you can answer the questions that matter during a review or investigation: which identities have broad administrative access, which agents are running on identities that can impersonate others, and which custom roles carry highly privileged access.
An Exposed Credential Has an Access Story
The same context changes how you understand an exposed credential.
Two leaked credentials can look identical from a secrets perspective. One belongs to an identity with read access to a development resource, so the damage it could do is limited. The other belongs to an identity with administrative access to production, sensitive permissions over IAM, or the ability to impersonate others. That one can open a much broader path into your environment.
Hush already shows you where a credential was found and how it’s being used. Now it also shows what the identity behind it could unlock if that credential were compromised, helping you understand the potential blast radius and prioritize the exposures that matter most.
By connecting Entitlements with the identities that hold the access and the credentials, workloads, and agents that use those identities, Hush makes it easier to identify risky access patterns in context: overly broad administrative access, impersonation capabilities, identities that can grant access to others, and custom roles with highly privileged permissions.
You see not just that risky access exists, but which identities hold it, how it can be used, and what it could affect.
Know the Agent. Know the Identity. Understand the Reach.
Agent security starts with discovery, but it can’t end there. Understanding an agent means understanding the identities and credentials it relies on, and understanding those identities means knowing the access they carry.
Hush brings agent discovery, NHI discovery, credentials, and Entitlements together into one picture of what an agent can reach and what it can do when it gets there.
Finding the agent gives you visibility. Understanding its access gives that visibility meaning.